
The Privileged Key
$19Opens every door in the cluster.
Engraved stainless steel. Fits a standard ring.
A container that runs privileged can reach the host kernel, and most teams discover which workloads do only when they look.
Add to cartRuntime Hardware Co. — est. in production
Software catches what software expects. These are the objects for what happens anyway: the process that appears at 04:12, the shell that nobody opened, the pod that was gone before anyone collected anything. Every item is fictional. Every problem is not.
Opens every door in the cluster.
Engraved stainless steel. Fits a standard ring.
A container that runs privileged can reach the host kernel, and most teams discover which workloads do only when they look.
Add to cart
Maybe it fits this time.
Boucle cover. Memory foam, obviously.
The kernel kills a process when its limit is reached, not when it is about to be reached. The last request is the one that does not get served.
Add to cart
A syscall allowlist you can frame.
A2, matte. Frame not included.
A syscall filter is only as useful as the list of calls your workload actually makes. Most of that list is shorter than teams expect.
Add to cart
Chimes on every exec.
Brushed aluminium tubes, bamboo disc.
A shell inside a container is a specific syscall with a parent process behind it. Which is the part an event log alone will not tell you.
Add to cart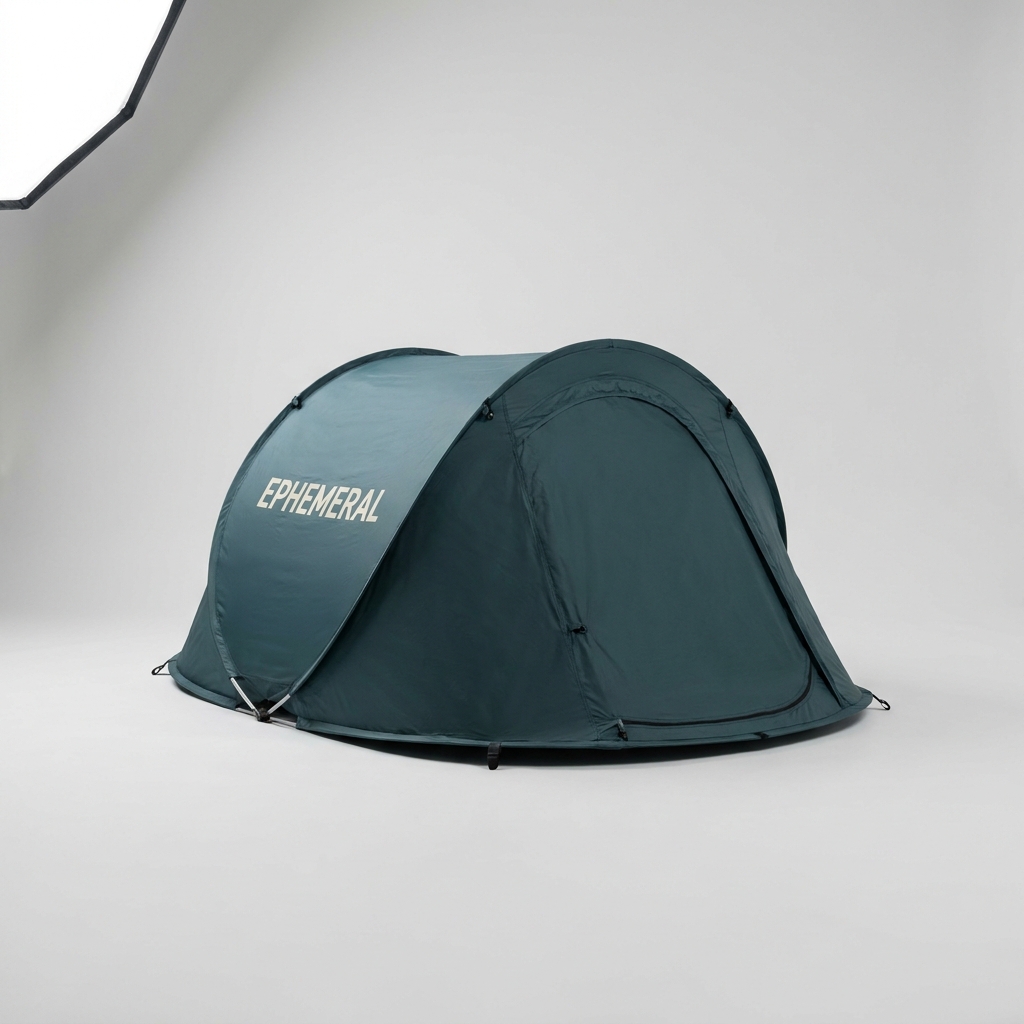
Pitches in seconds. Disappears on exit.
One person. No floor.
Debug containers are the most privileged thing in most clusters and the least governed: no image to scan, no baseline, no ticket.
Add to cart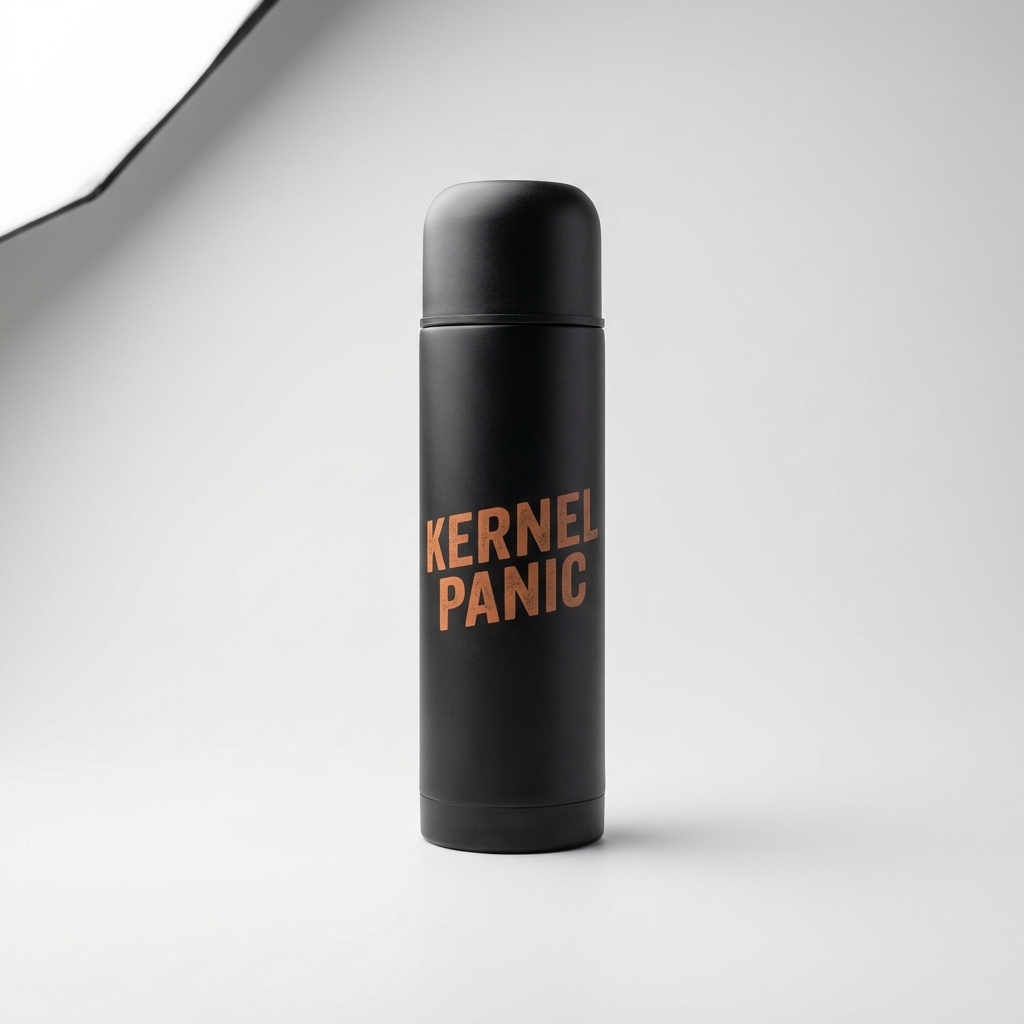
Keeps it hot until 04:12.
500 ml. Leak-proof up to the point it matters.
The host that carries your workloads is a different blast radius from the workload itself, and almost nothing reports on it.
Add to cart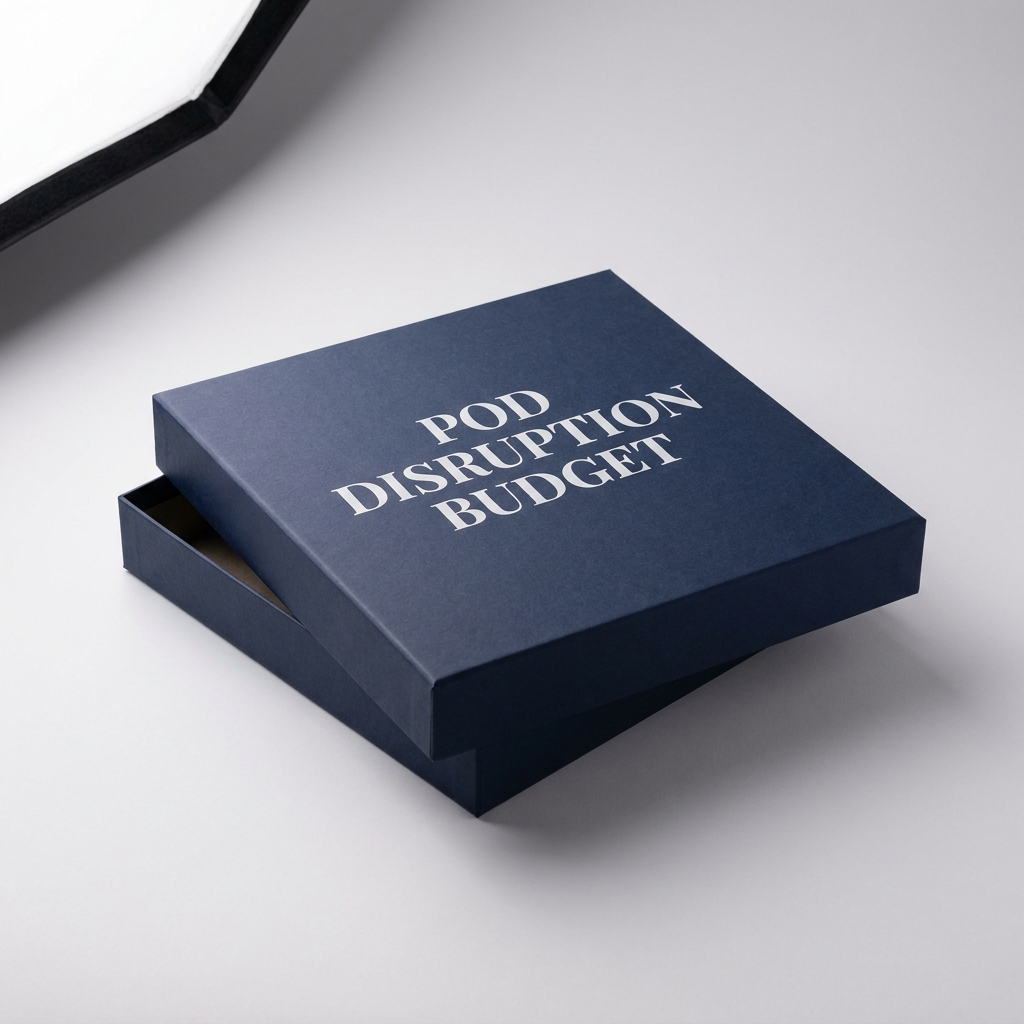
Lose the game, lose a pod.
2-5 players. 40 minutes. No volunteers.
A budget that is never tested is a number, not a guarantee. The rotation that takes a node out is the test.
Add to cart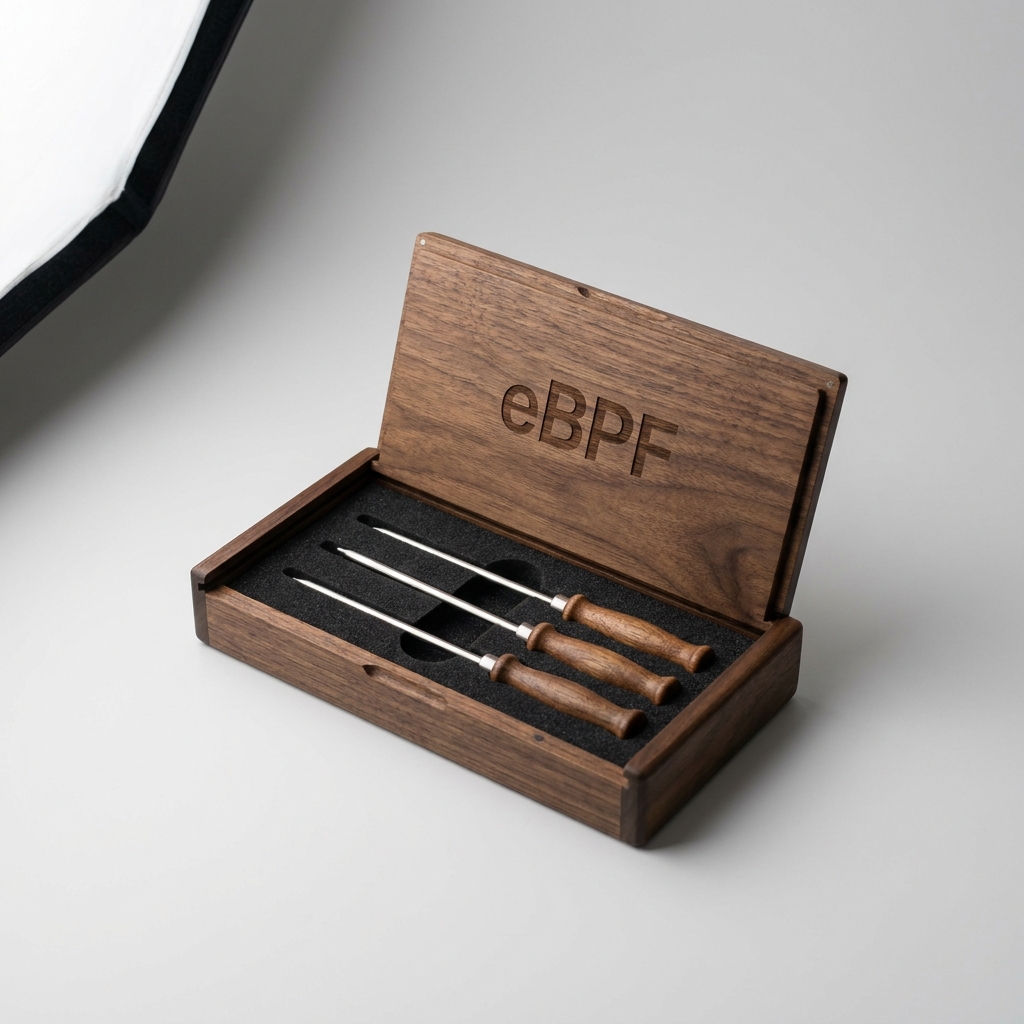
For going deeper into the kernel.
Three probes, fitted case. Requires root.
The only account of what a process did that the process cannot rewrite is the one taken at the syscall, below it.
Add to cart
Write once. Regret forever.
A5, 192 pages, immutably blank.
A container with a read-only root filesystem removes a whole class of post-exploitation, and costs almost nothing to run.
Add to cart
Time is an illusion.
Silent movement. Very silent.
The image that never arrives fails louder than the image that arrives compromised. Only one of those shows up on a dashboard.
Add to cart
Leave your capabilities at the door.
Pair, sterling. 41 available, usually granted.
Defaults hand a process capabilities it never calls. Dropping them is one line in a manifest and one fewer path after a compromise.
Add to cart
Scheduling your morning.
300 ml. Taints: caffeine.
When a node goes NotReady, what happened on it during the last minutes before is the question nobody can answer afterwards.
Add to cartCheckout
We could ship you a keychain. What we actually ship is the answer to the question every product above is a joke about: what did this process do while it was running, and can anyone prove it afterwards?
That is Primod: a runtime security platform for Kubernetes and container workloads. It watches what workloads execute — the syscall, the parent process, the file that was read — and turns it into evidence an investigator can defend in a review.
Runtime Hardware Co. is a marketing artifact published by Primod. No order will be fulfilled, no card will be charged, and no keychain has ever been manufactured. The failure modes are real and documented in our posts.