Author

Author profile

Abdullah Kucukoduk

CTO, PrimodIstanbul, TR

Abdullah Kucukoduk is CTO at Primod, where he leads the technical development of the runtime security platform: the eBPF sensor, the event pipeline behind it, and the investigation and vulnerability workflows built on top.
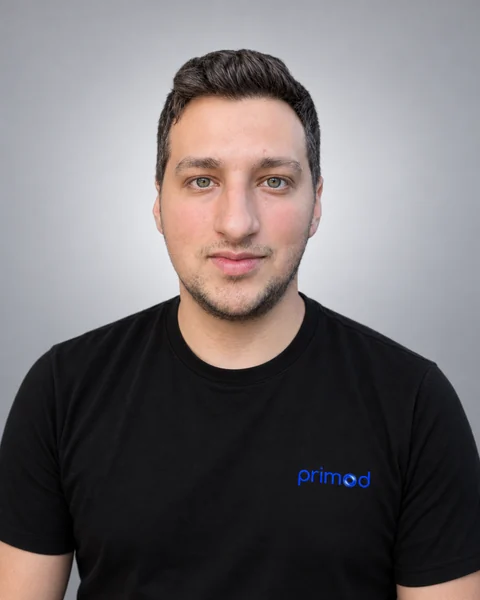
Abdullah Kucukoduk, CTO, Primod

Expertise

What he's responsible for

01

Technical direction

He sets the architecture of Primod's runtime security platform and owns the trade-offs behind it: what the sensor observes, what the platform keeps, and what it refuses to guess.

02

Runtime evidence as a discipline

His position is that a security decision should rest on what actually executed in production. It shapes every product call he makes, from how findings are ranked to what an investigation shows first.

03

Engineering under production constraints

He holds the eBPF sensor and the pipeline behind it to the budget of the workloads they run on. Overhead, noise, and operability are requirements he owns, not metrics he reports.

04

The engineering team and its standards

He leads the engineers building the platform and is accountable for how it is built: instrumented, debuggable, and safe to operate by people who did not write it.

Published insights
Articles by Abdullah Kucukoduk

All articles
Release9 minPrimod 2026.10.0: See the Request, the Code and the Cloud Behind Every AttackPrimod 2026.10.0 is here: cases with the evidence already attached, runtime reachability for every CVE, a traffic map that names your apps, and attack graphs for AWS, Azure and Google Cloud.October 13, 2026Read Comparison8 minPrimod vs Falco: Features and TradeoffsFalco is an open-source detection engine you run and tune yourself. Primod is a commercial runtime security platform built around the investigation. A fair comparison of what each gives a security team.September 6, 2026Read Comparison8 minPrimod vs Tetragon: Features and TradeoffsTetragon gives platform teams precise eBPF observability and in-kernel enforcement through tracing policies. Primod adds the investigation and vulnerability workflows on top of a sensor. Where each fits.September 6, 2026Read Guide9 minFalco vs Tetragon (2026): detection vs enforcementPick Falco for rule-driven threat detection and alerting. Pick Cilium Tetragon when you need kernel-level eBPF observation and in-kernel enforcement.September 6, 2026Read Security9 minSBOMs and VEX Still Need Runtime Context in KubernetesSBOMs tell you which components are present. VEX tells you whether a supplier says a product is affected. Neither can prove whether a vulnerable path executed in your cluster, which is why platform teams should separate supply-chain assertions from runtime evidence.March 18, 2026Read Security8 minAdmission Control Stops Bad Specs, Not Bad Runtime BehaviorPod Security Admission, CEL policies, and admission webhooks can reject unsafe manifests before they land in etcd. They still do not tell you what a workload executed after startup, which is why platform teams should separate preventive policy from runtime evidence.March 11, 2026Read Engineering4 minHow to Measure eBPF Overhead on KubernetesA practical guide to comparing eBPF telemetry overhead: control the workload, measure CPU, memory and latency, and check event loss before rollout.February 18, 2026Read Security8 minWhy CVSS Scores Fail Platform Teams and What Runtime Reachability FixesA CVE with a 9.8 score that never executes in your environment is less dangerous than a 5.3 that runs on every request. We built a scoring model around this idea.February 11, 2026Read Incident Response4 minScoping Incidents With Runtime EvidenceUse process activity, workload identity and event outcomes to scope an incident, record uncertainty, and hand the evidence to the responding team.February 4, 2026Read Engineering7 minBlast Radius Estimation With Cloud Posture and Service LineageKnowing a vulnerability is reachable is step one. Knowing which downstream services it can propagate to is what turns a finding into a prioritized action.January 28, 2026Read Architecture13 minKernel Probes vs Sidecar Proxies: A Telemetry Architecture ComparisonTwo fundamentally different approaches to runtime visibility. One lives in the kernel, one lives next to your container. We compare latency, fidelity, and operational cost.January 21, 2026Read Compliance6 minContinuous SOC2 Evidence Collection With Runtime TelemetryAudit season should not mean two weeks of manual log exports. Here is how runtime execution data maps to SOC2 CC6 controls and what auditors actually ask for.January 14, 2026Read